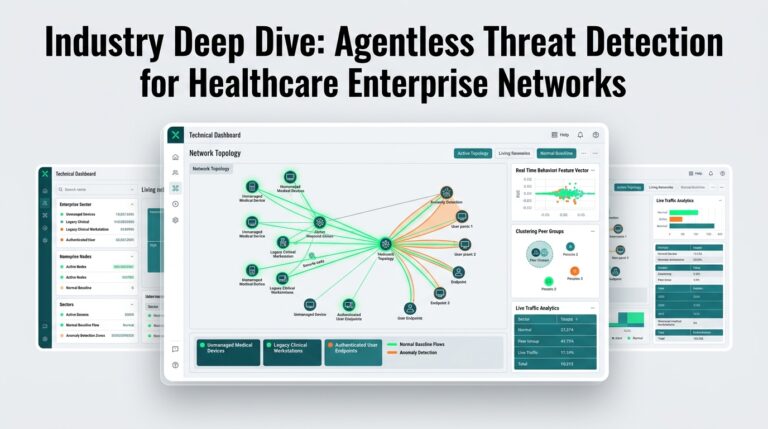
Healthcare Agentless Behavioral Threat Detection Architecture
Agentless behavioral threat detection turns raw network telemetry into actionable intelligence, revealing insider threats and credential misuse across healthcare networks without endpoint software agents.
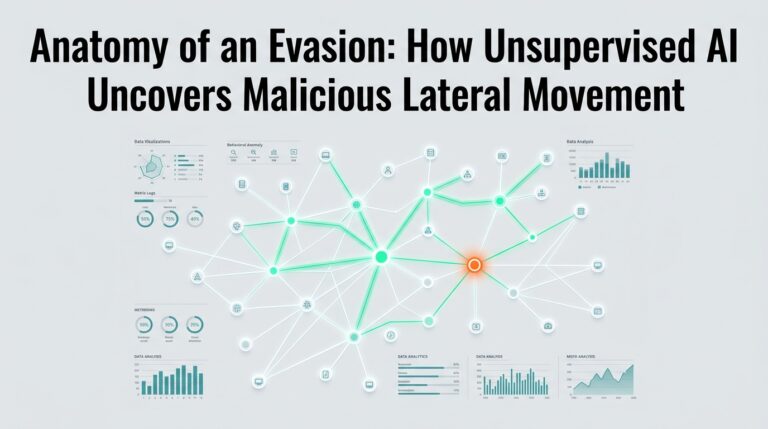
Detecting Living-off-the-Land Lateral Movement | Personam AI
Adversaries using legitimate administrative tools often bypass legacy EDR and SIEM defenses. Unsupervised network behavioral AI detects subtle cohort anomalies to intercept lateral movement before…
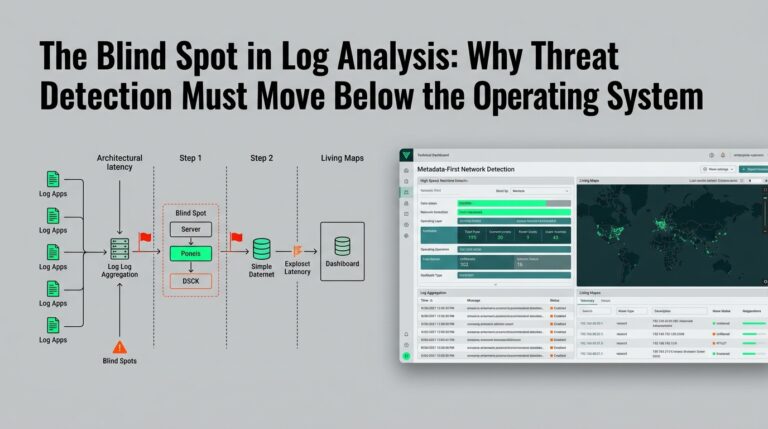
Why Log Aggregation Fails: Real-Time Metadata-First NDR
Log files are downstream, derivative, and easily cleared by adversaries. Learn how metadata-first NDR operates below log files to detect threats within seconds.
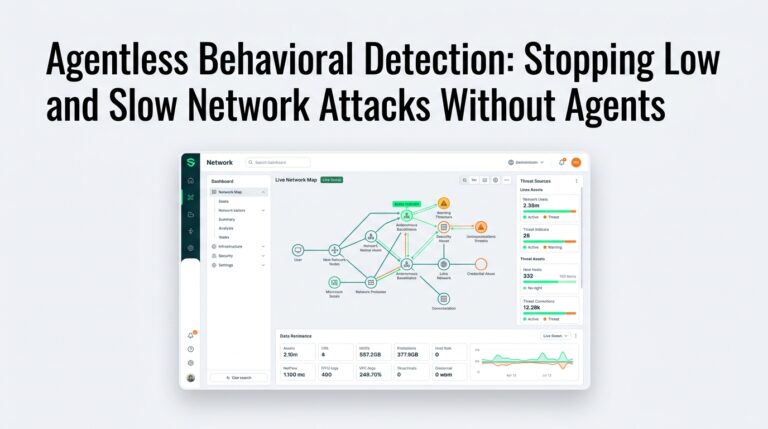
Agentless Behavioral Detection | Stop Low & Slow Attacks
Personam delivers agentless behavioral detection that stops low and slow network attacks and living-off-the-land tradecraft without host software or complex rule tuning.
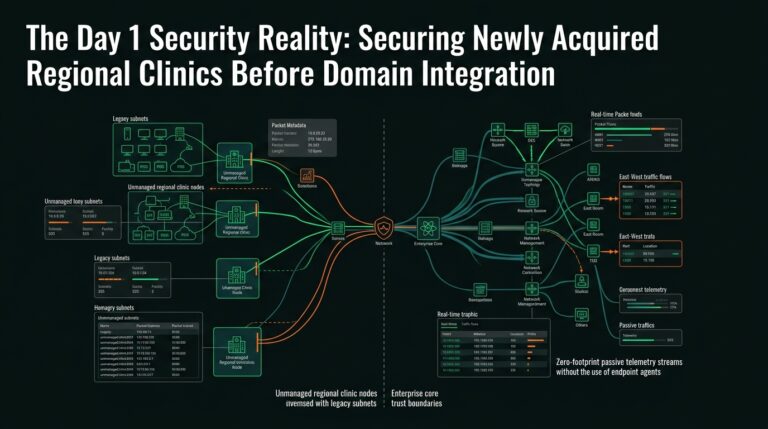
Securing Acquired Regional Clinics Before Domain Integration
Healthcare mergers create immediate cybersecurity exposure across transitional network connections. Learn how agentless behavioral telemetry provides instant visibility and stops cross-domain credential abuse on Day…
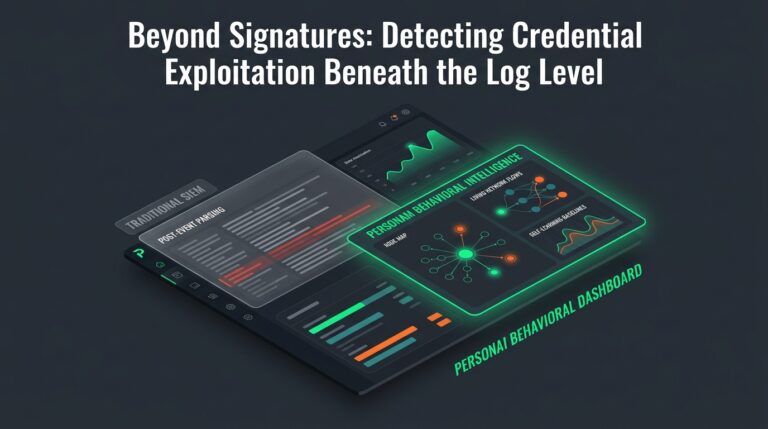
Beyond Signatures: Credential Exploitation Beneath Log Level
Legacy SIEMs fail when adversaries use valid credentials and native OS tools. Personam provides agentless behavioral intelligence to expose credential exploitation beneath the log level…
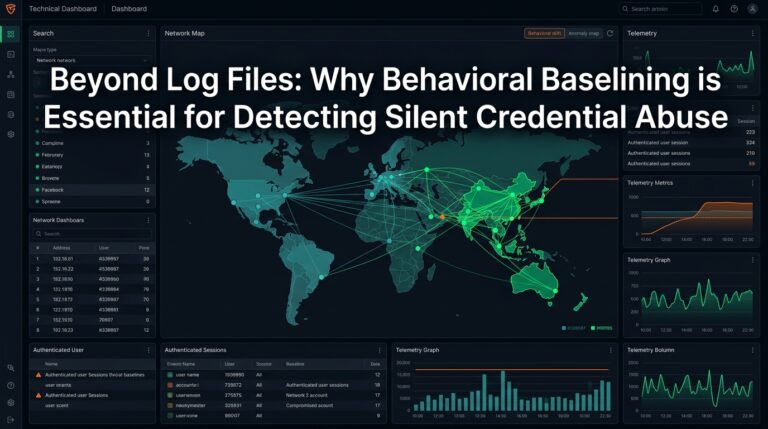
Beyond Log Files: Behavioral Baselining for Credential Abuse
Traditional SIEM log analysis and static correlation rules are blind to attackers operating with valid credentials. Continuous behavioral baselining inspects network traffic layers below log…
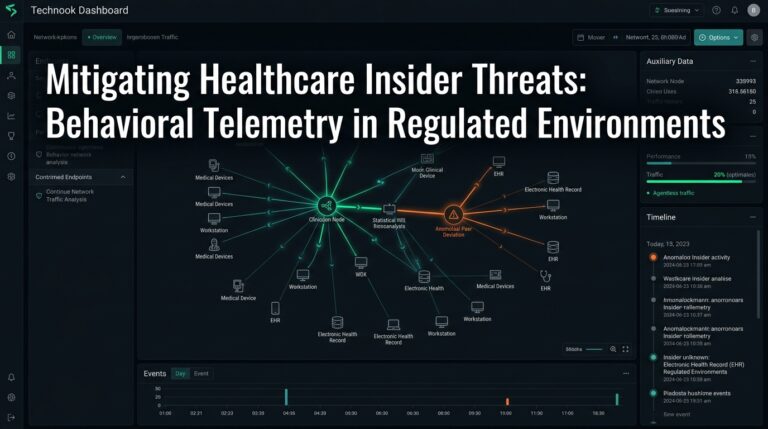
Mitigating Healthcare Insider Threats via Behavioral Telemetry
Securing EHR environments against compromised credentials requires continuous, agentless behavioral telemetry. Learn how peer baselining stops unauthorized lateral movement without disrupting clinical care.
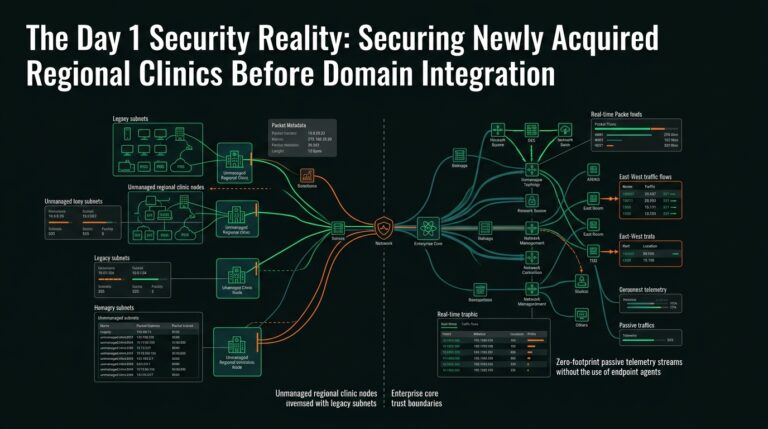
Securing Acquired Regional Clinics Before Domain Integration
Healthcare acquisitions create immediate network visibility gaps before Active Directory consolidation. Agentless behavioral telemetry provides Day 1 threat detection without relying on endpoint agents or…
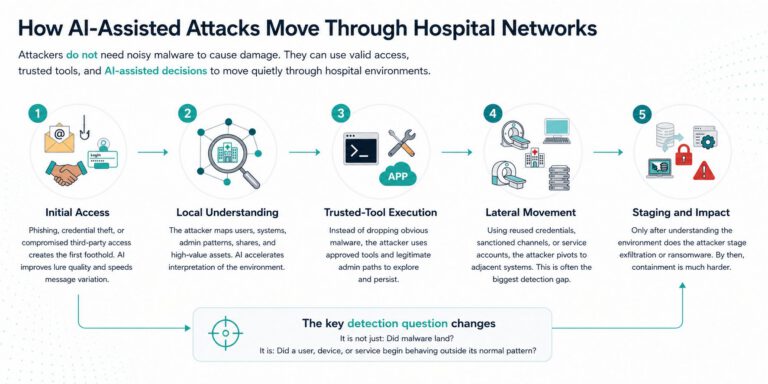
When Trusted Tools Turn Hostile: AI-Assisted Lateral Movement in Hospital Networks
The most dangerous hospital attacks don't start with obvious malware. They start with valid credentials, normal-looking administrative activity, and tools the organization already trusts. AI…