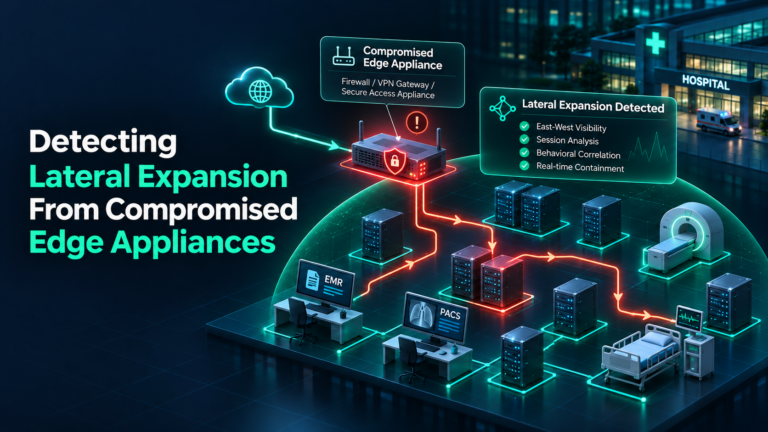
Detecting Lateral Expansion From Compromised Edge Appliances
Edge appliances sit under constant targeting. Attackers actively scan the internet for known vulnerabilities in enterprise VPN gateways, remote access portals, and edge firewalls. When…
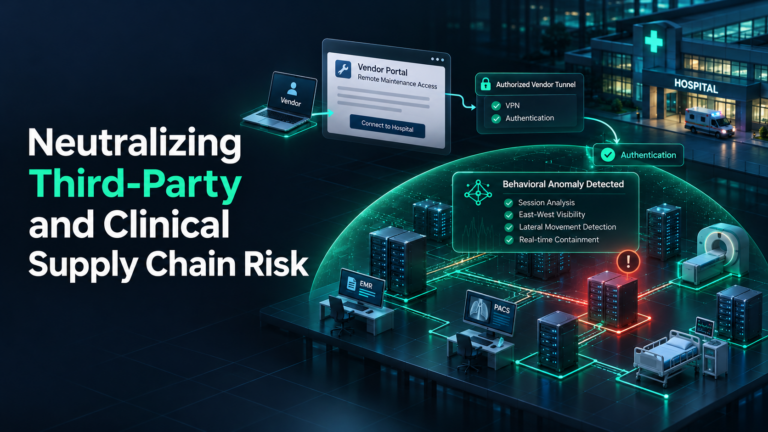
Neutralizing Third-Party and Clinical Supply Chain Risk
Healthcare delivery systems run on interconnected dependencies. Clinical diagnostic tools, remote radiology reading stations, outsourced billing services, and HVAC controls connect directly to internal hospital…
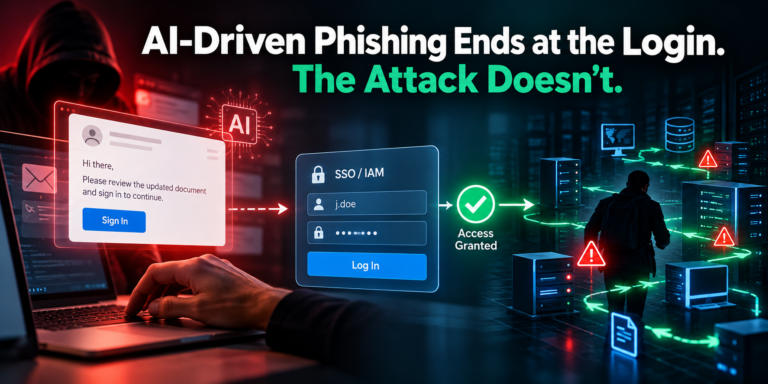
AI-Driven Phishing Ends at the Login. The Attack Doesn’t.
Generative AI has fundamentally changed initial access mechanics. Attackers no longer rely on poorly worded emails or obvious phishing links to harvest credentials. AI-assisted campaigns…
Intercepting Ransomware Outages at the Wire Layer
Ransomware operations across healthcare facilities no longer begin with noisy, immediate file encryption. Modern Ransomware-as-a-Service (RaaS) affiliates operate with calculated restraint. Upon breaching an entry…
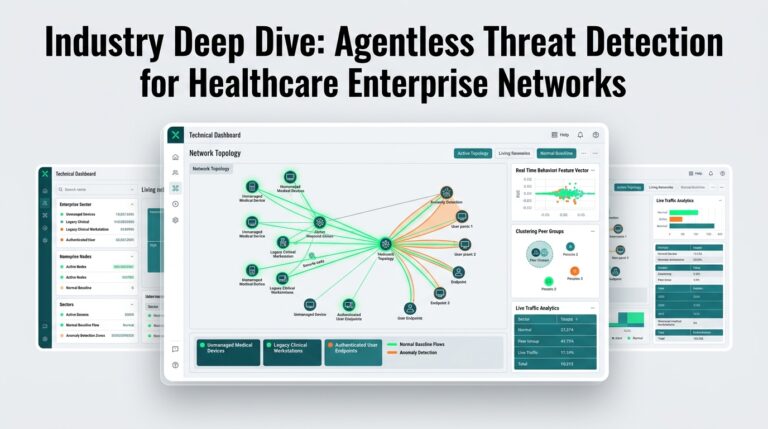
Healthcare Agentless Behavioral Threat Detection Architecture
Agentless behavioral threat detection turns raw network telemetry into actionable intelligence, revealing insider threats and credential misuse across healthcare networks without endpoint software agents.
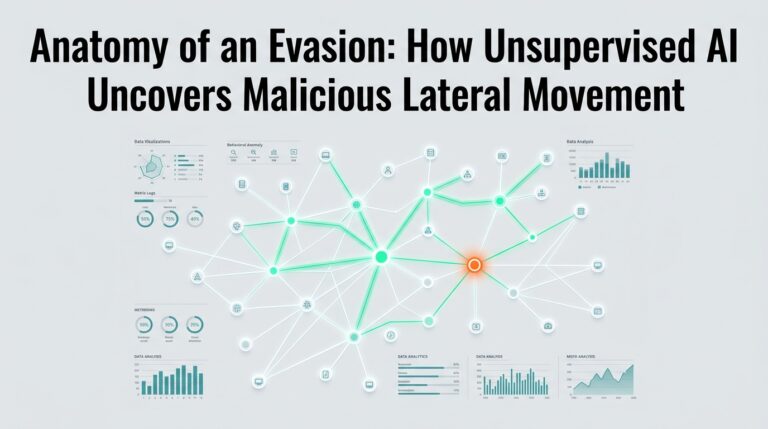
Detecting Living-off-the-Land Lateral Movement | Personam AI
Adversaries using legitimate administrative tools often bypass legacy EDR and SIEM defenses. Unsupervised network behavioral AI detects subtle cohort anomalies to intercept lateral movement before…
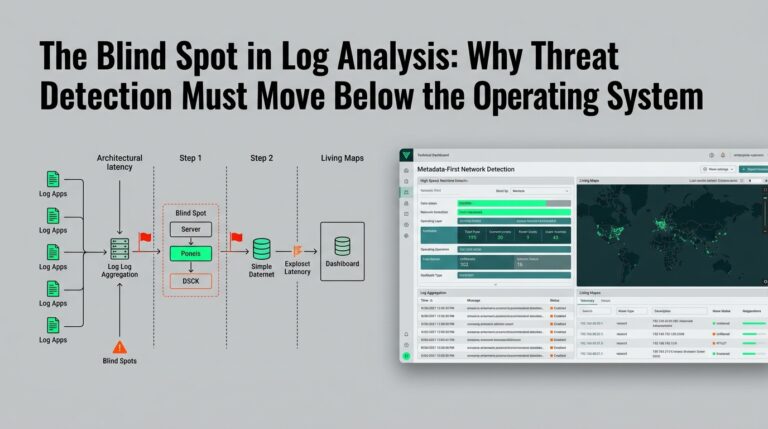
Why Log Aggregation Fails: Real-Time Metadata-First NDR
Log files are downstream, derivative, and easily cleared by adversaries. Learn how metadata-first NDR operates below log files to detect threats within seconds.
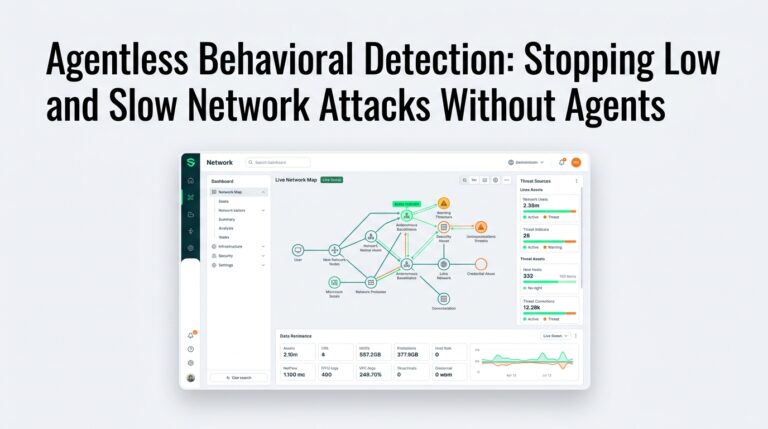
Agentless Behavioral Detection | Stop Low & Slow Attacks
Personam delivers agentless behavioral detection that stops low and slow network attacks and living-off-the-land tradecraft without host software or complex rule tuning.
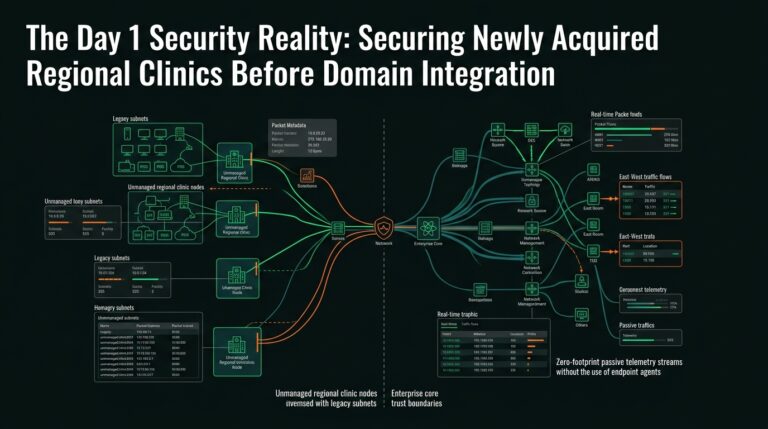
Securing Acquired Regional Clinics Before Domain Integration
Healthcare mergers create immediate cybersecurity exposure across transitional network connections. Learn how agentless behavioral telemetry provides instant visibility and stops cross-domain credential abuse on Day…
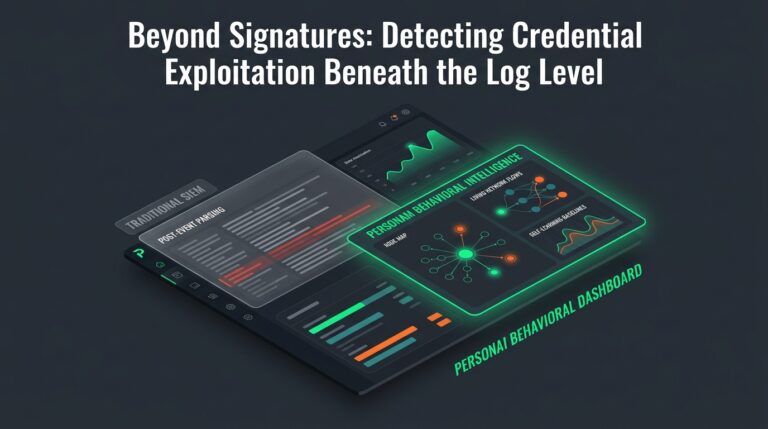
Beyond Signatures: Credential Exploitation Beneath Log Level
Legacy SIEMs fail when adversaries use valid credentials and native OS tools. Personam provides agentless behavioral intelligence to expose credential exploitation beneath the log level…