Beyond Log Files: Behavioral Baselining for Credential Abuse
Traditional SIEM log analysis and static correlation rules are blind to attackers operating with valid credentials. Continuous behavioral baselining inspects network traffic layers below log…
Mitigating Healthcare Insider Threats via Behavioral Telemetry
Securing EHR environments against compromised credentials requires continuous, agentless behavioral telemetry. Learn how peer baselining stops unauthorized lateral movement without disrupting clinical care.
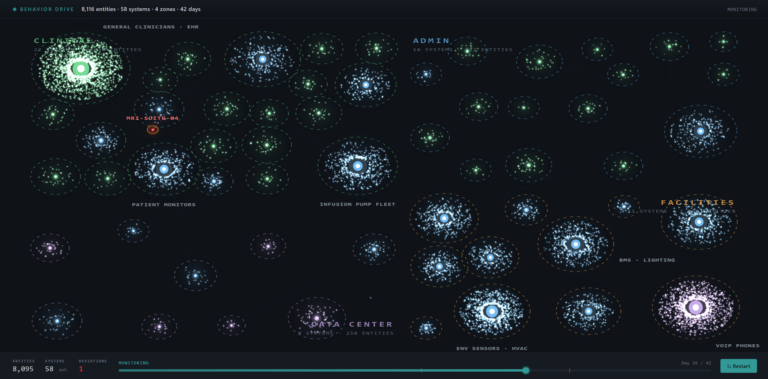
The Limits of Legacy Network Security: Why Behavioral Detection Must Evolve
Modern threat actors don’t break in. They log in. When adversaries use valid credentials, native administrative tools like PowerShell or WMI, and approved network protocols,…
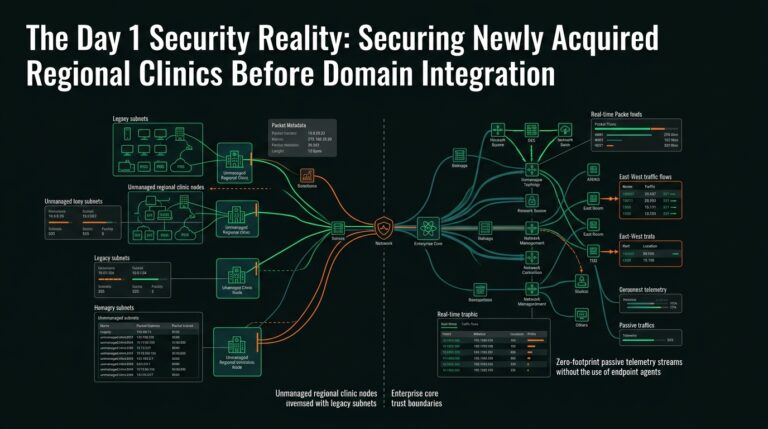
Securing Acquired Regional Clinics Before Domain Integration
Healthcare acquisitions create immediate network visibility gaps before Active Directory consolidation. Agentless behavioral telemetry provides Day 1 threat detection without relying on endpoint agents or…
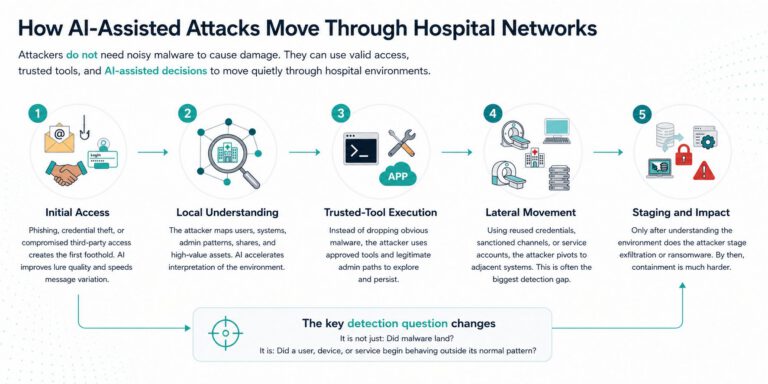
When Trusted Tools Turn Hostile: AI-Assisted Lateral Movement in Hospital Networks
The most dangerous hospital attacks don't start with obvious malware. They start with valid credentials, normal-looking administrative activity, and tools the organization already trusts. AI…
Why Signal Quality is the Real ROI in Healthcare Cybersecurity
Hospitals don't need more alerts. They need better ones. A quantified look at what alert noise costs, and what clarity recovers.
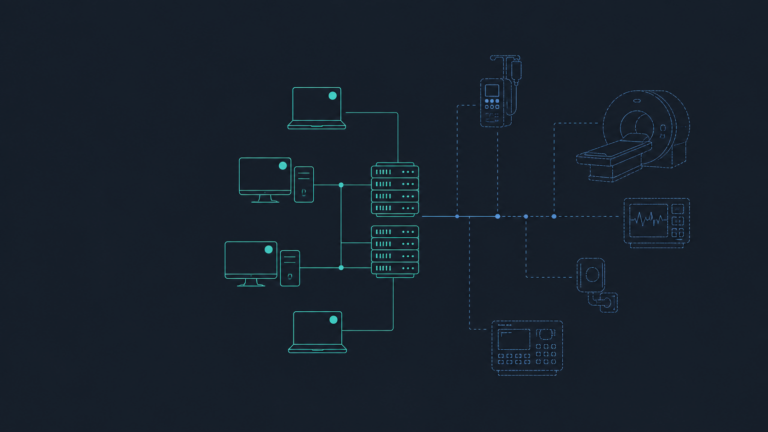
The Unagentable Blind Spot: Why CISOs Need Network-Level Visibility in Healthcare
96% of hospitals run end-of-life systems. Active scanning disrupts medical devices. The threat path is behavior, not malware, and your endpoint-first controls have a blind…
Living Off the Land: The “Ghost” Cyber Attack Healthcare Teams Are Struggling to See
No malware. No suspicious executable. Attackers use the tools already inside your environment, and traditional tools treat it as normal administration.