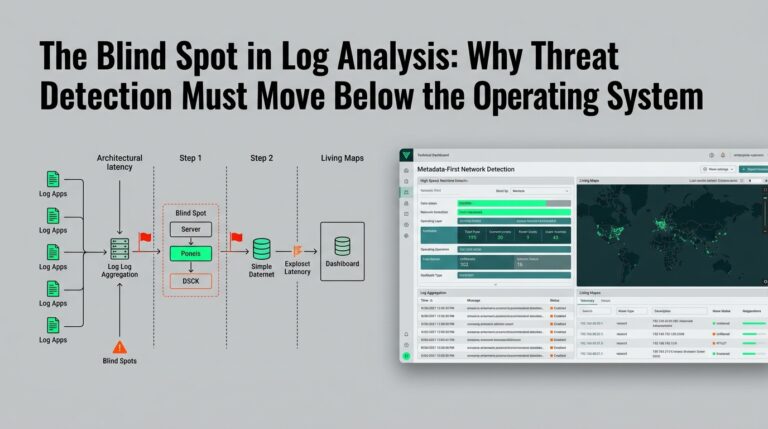
Network Data Doesn't Lie
Why Log Aggregation Fails: Real-Time Metadata-First NDR
Log files are downstream, derivative, and easily cleared by adversaries. Learn how metadata-first NDR operates below log files to detect threats within seconds.
Insider Threat
Beyond Signatures: Credential Exploitation Beneath Log Level
Legacy SIEMs fail when adversaries use valid credentials and native OS tools. Personam provides agentless behavioral intelligence to expose credential exploitation beneath the log level…
Healthcare Security
Beyond Log Files: Behavioral Baselining for Credential Abuse
Traditional SIEM log analysis and static correlation rules are blind to attackers operating with valid credentials. Continuous behavioral baselining inspects network traffic layers below log…